This cheat sheet outlines how responders can review logs during a security incident. It covers which logs to gather, how long they last, and how to spot log tampering. It also lists what to look for in identity, cloud, network, web, Windows, and Linux logs.
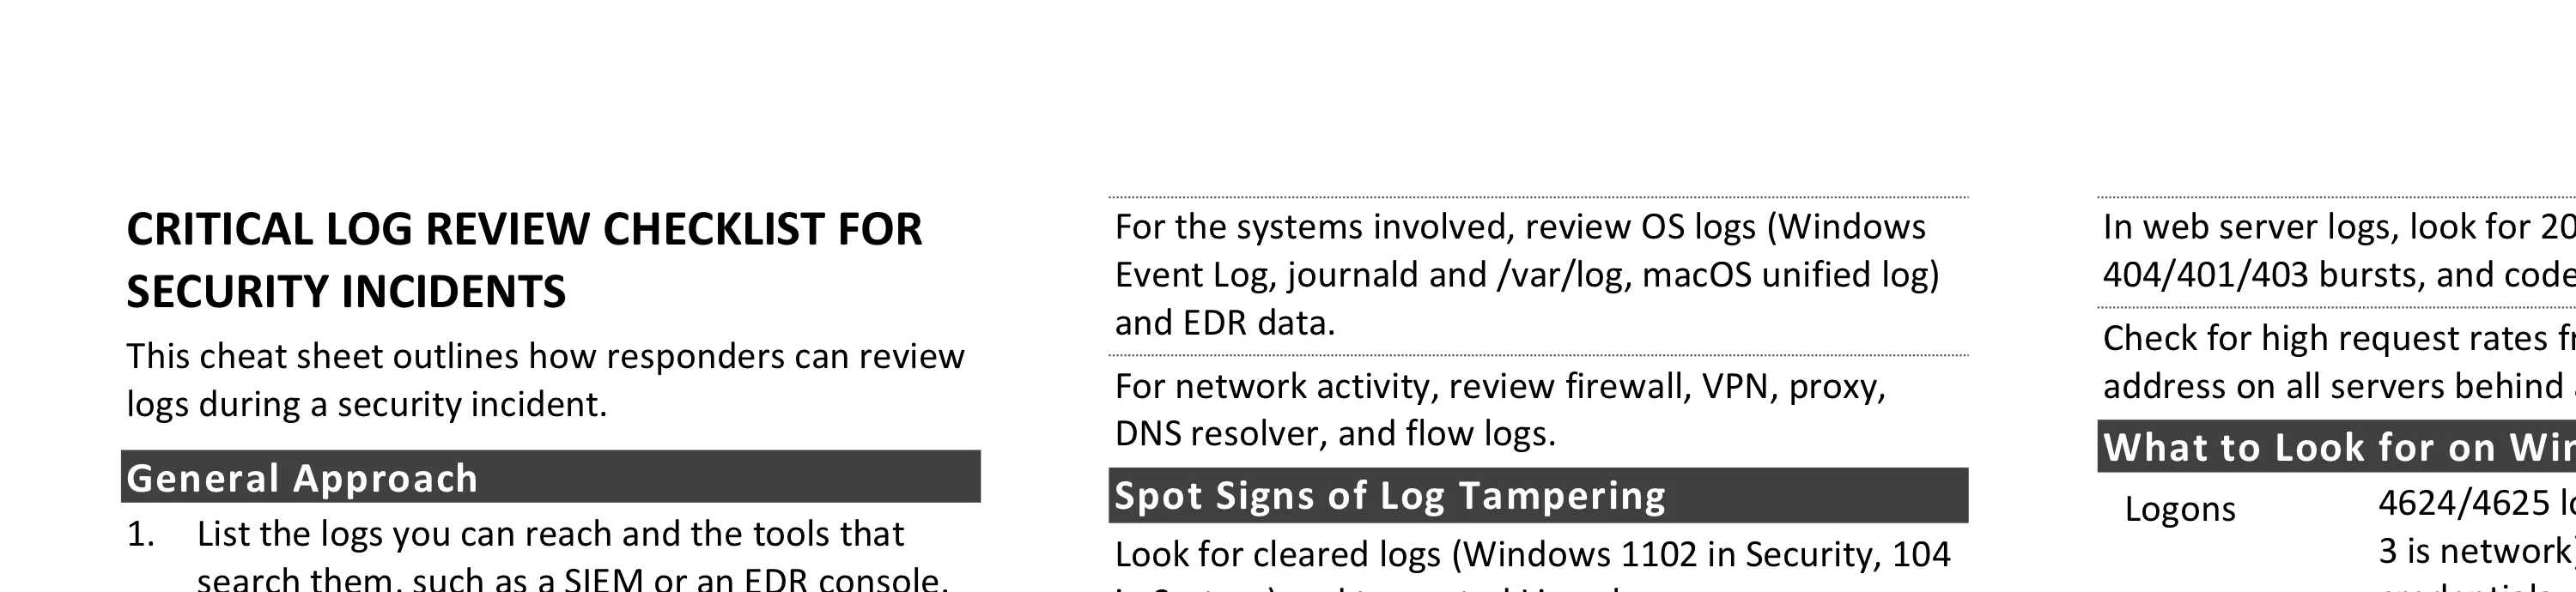
This cheat sheet outlines how responders can review logs during a security incident. To print, use the one-page PDF version. You can also edit the Word version for your own needs. It pairs with the Security Incident Survey Cheat Sheet for System Administrators and the Initial Security Incident Questionnaire for Responders.
General Approach
- List the logs you can reach and the tools that search them, such as a SIEM or an EDR console.
- Preserve logs that might expire soon, then start with the relevant logs you can search fastest.
- Confirm you can trust each source’s timestamps, and convert them to UTC in your timeline.
- Check each source’s retention and ingestion delay, since older logs can expire and new ones might arrive late.
- Remove routine, repetitive entries from view once you’ve confirmed they’re benign.
- Focus on recent changes, failures, admin and access events, and anything unusual.
- Work backwards from the security alert or report to reconstruct what happened before and after it.
- Trace suspicious accounts, hosts, or addresses across logs to confirm or rule out your theories.
Log Sources and Their Retention
- Export identity logs (Entra ID, Okta, Google Workspace) early unless the SIEM has them.
- Cloud audit logs (CloudTrail, Azure Activity Log, Cloud Audit Logs) cover admin actions by default. Data access logging is often off.
- Check the audit logs of affected business apps, such as Microsoft 365, for forwarding rules, sharing, and admin changes.
- For phishing, check message trace logs for recipients and URL protection logs for clicks.
- For the systems involved, review OS logs (Windows Event Log, journald and /var/log, macOS unified log) and EDR data.
- For network activity, review firewall, VPN, proxy, DNS resolver, and flow logs.
Spot Signs of Log Tampering
- Look for cleared logs (Windows 1102 in Security, 104 in System) and truncated Linux logs.
- Look for audit policy changes (Windows 4719), stopped log agents or EDR sensors, and cloud audit logging turned off.
- Look for gaps in a log’s record IDs or in time from a host that logged steadily before.
- Rule out rotation and ingestion failures, then rebuild the gap from flow records or peer systems’ logs.
What to Look for in Identity and Cloud
- Look for sign-ins from a new country or device, impossible travel, failures then a success, or no MFA.
- Check non-interactive sign-ins too, such as service principals and tokens from unfamiliar addresses.
- Review MFA methods added or removed, recovery contacts changed, and passwords reset by an admin.
- Review OAuth consents, new app credentials, API tokens, admin roles, IAM policies, and access keys.
- Look for signs of data theft, such as mass downloads from internal stores, database exports, and storage made public.
What to Look for on the Network and Web
- Look for new inbound addresses, outbound connections from servers that rarely make them, and VPN logins from unexpected countries.
- Look for DNS queries to random-looking domains, large uploads to file sharing sites, and regular connections to one destination.
- In web server logs, look for 200s for unknown files, 404/401/403 bursts, and code in URLs.
- Check for high request rates from one API token or address on all servers behind a load balancer.
What to Look for on Windows
| Event | IDs |
|---|---|
| Logons | 4624/4625 logons (type 10 is RDP, 3 is network), 4648 explicit credentials, 4672 special privileges |
| Accounts | 4720 created, 4724 password reset, 4726 deleted, 4740 lockout |
| Groups | 4728/4732/4756 member added |
| Persistence | 4698 task created, 4702 updated, 7045 new service (System) |
| Execution (if enabled) | 4688 process, 4104 PowerShell, Sysmon 3 network connection |
| Domain controllers | 4768/4769 Kerberos tickets, 4771 pre-auth failed, 4776 NTLM |
| Defender | 1116 malware detected, 1117 action taken (Defender log) |
What to Look for on Linux
| Event | Log Entry |
|---|---|
| Logins | “Accepted …”, “session opened” |
| Failed logins | “Failed password”, “Invalid user” |
| Privilege use | “FAILED SU”, “sudo … COMMAND=” |
| Accounts | “new user”, “add … to group” |
| Persistence | crontab “REPLACE”, systemd and authorized_keys edits if audited |
Other Resources
- Microsoft’s events to monitor, the Windows Security Log Encyclopedia, Sigma with Hayabusa, and CISA’s logging guidance.
- Companion Security Incident Survey Cheat Sheet, Initial Security Incident Questionnaire, and incident response report template.
Post-Scriptum
Anton Chuvakin and I wrote the 2010 version of this checklist, which Anand Sastry reviewed. I revised it in 2026. The log tampering and cloud logging points are adapted from Dynamic Incident Response by Joshua Wright (CC BY 4.0). If you have suggestions for improving this cheat sheet, please let me know. This cheat sheet is distributed under the Creative Commons Attribution 4.0 International License. Take a look at my other security cheat sheets.